
HodeiShield
Compliance you can prove. Risk you can see. Suppliers you can trust.
0points
Details
Launched
November 4, 2026
Category
AI & Machine Learning
Tags
aiautomationgdprreportssecurity
About HodeiShield
HodeiShield is a cyber risk and compliance platform for European companies that need to prove their security, not just claim it, under DORA, NIS2, ENS, ISO 27001, the EU AI Act and more.
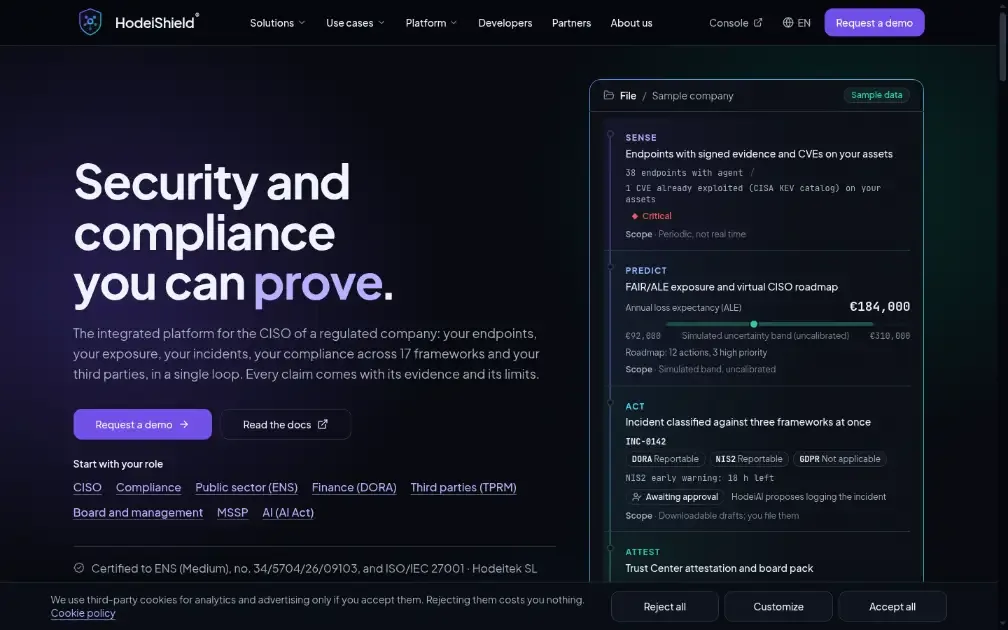
It brings together what most teams run across spreadsheets, email and five different tools (compliance, suppliers, exposure, incidents, endpoints and board reporting) into one continuous cycle with four pillars.
SENSE: see your real exposure
- External exposure radar. Certificates, ports, headers and CVEs checked from the outside, with nothing asked of the supplier.
- Supply chain and SBOM. Get alerted when a new vulnerability affects a component or supplier you depend on.
- Endpoint security. A lightweight agent that reports device posture, with signed attestations.
PREDICT: understand the risk before it hits
- Third-party risk. Explainable risk scores for every supplier, with the breakdown and the trend.
- Multi-framework compliance. Map one control and one piece of evidence across DORA, NIS2, ENS and ISO 27001 instead of documenting it four times.
ACT: respond, with a human in the loop
- Incident management. Classify an incident and see the DORA and NIS2 notification deadlines, with the authority report generated from it.
- Supplier questionnaires. Answered on a portal, with evidence attached.
- AI governance. Register the AI systems your organisation uses and manage your EU AI Act obligations.
- Virtual CISO and HodeiAI. Guidance and an AI assistant that work on your own data. They suggest the next step; they don’t act on their own.
ATTEST: prove it to others
- DORA Register of Information. Generate it as an xBRL-CSV package with the EBA structure.
- Board reports. A readable view of cyber risk for management and the board.
- Trust Center and Attest. Publish your security posture, with evidence whose integrity and origin can be verified cryptographically.
Why trust it
- Open by design. A public, open-source verifier and a read-only CLI with signed releases (Sigstore, SLSA).
- EU and certified. Hosted in the EU. Operated by Hodeitek, certified ISO 27001 and ENS (Medium), with HodeiShield in scope.
For MSSPs: one console for many client tenants, each strictly isolated, with free proof-of-concepts for partners.
The beta is open. Join it and start with your first framework or your first suppliers.
What HodeiShield does
HodeiShield brings security, compliance, and third-party risk into one cycle for security leads at regulated companies. It collects evidence from endpoints and suppliers, maps that evidence to controls across 17 frameworks, quantifies exposure in euros using FAIR, and supports incident management and board reporting. The platform addresses fragmented, outdated records by assigning evidence an owner, validity date, and status, and by issuing attestations that can be verified offline. The page says audit readiness depends on the organisation’s evidence.
A Windows, macOS, or Linux agent runs checks and sends digitally signed observations, which the console verifies. HodeiShield maps evidence to framework controls and reuses it across frameworks; expired evidence stops counting. PREDICT estimates FAIR/ALE exposure with a simulated, uncalibrated uncertainty band. HodeiAI proposes actions, but a user with a write role must approve execution; the only executable action currently described is creating a risk-register entry. ATTEST issues signed attestations that can be checked offline with a public verifier.
The page presents HodeiShield for security leads at regulated companies and describes testing with MSSP partners and organisations. Its scope includes endpoint security, exposure management, supply-chain and third-party risk, incident management, multi-framework compliance, and board reporting. It covers 17 frameworks, including NIS2, ENS, DORA, and ISO/IEC 27001. The platform keeps proposed actions subject to human approval and states that attestations prove integrity, origin, and time, not that their contents are true or a substitute for an audit.
Based on hodeishield.com, read on Nov 4, 2026.
Key features
- Collects signed endpoint evidence
- Maps evidence across 17 frameworks
- Quantifies exposure using FAIR/ALE
- Classifies incidents and prepares drafts
- Proposes actions for human approval
- Issues offline-verifiable attestations
What people use HodeiShield for
- 01Monitor endpoint posture and asset vulnerabilities
- 02Track evidence coverage across compliance frameworks
- 03Estimate cyber exposure in euros
- 04Classify incidents against DORA, NIS2, and GDPR
- 05Prepare board reports and attestations
More in AI & Machine Learning
Browse all AI & Machine Learning APIMart
 is a unified AI API platform that provides access to over 500 AI models,
 MojoMake AI Video & Image Studio
Generate AI video and image with Veo, Kling, Flux, and 15+ models — plus 100+ effects
 MusVideo
 is the AI music to video generator that turns your audio tracks into cinematic music videos
 Image Translator Pixel-Perfect
AI Image Translator is an advanced tool that utilizes AI to translate text within images
 GPT Image 2 - Advanced Image 2
Create and edit high-fidelity images with GPT Image 2, featuring accurate multilingual text
 Omni Flash
 is a multimodal AI video generator that produces cinematic 4K clips